Bridging It And Ot: Analyzing The French Supermarket Refrigeration Cyber Attack + Video
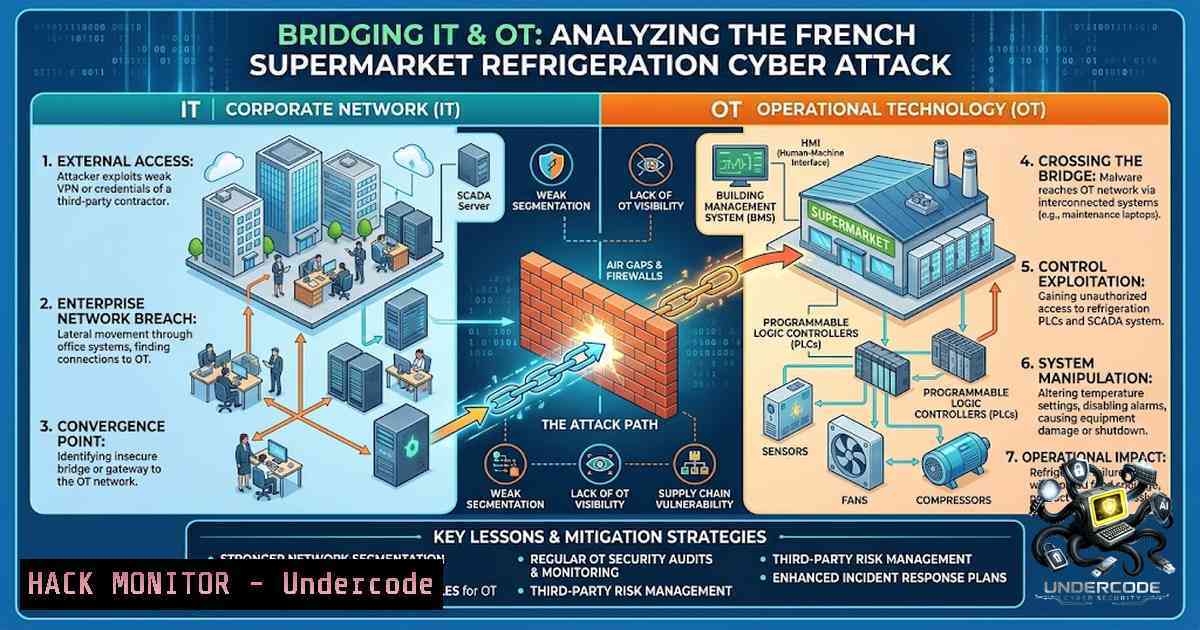
Introduction:
The recent cyber incident targeting supermarket refrigeration systems across France highlights the critical convergence of Information Technology (IT) and Operational Technology (OT). Attackers remotely manipulated controllers from major vendors like Danfoss, Copeland, and Dixell, forcing units into continuous defrost modes and elevating temperatures to 50°C, resulting in severe food spoilage and localized fires. This event underscores the urgent need for robust hardening, secure access design, and continuous monitoring of industrial control systems connected to public networks.
Learning Objectives & Secrets:
Objective 1: Understand how unauthenticated management interfaces and firmware vulnerabilities expose physical industrial refrigeration systems to remote cyber manipulation.
Objective 2 secret tips: Isolate OT networks from enterprise IT using hardened industrial firewalls, enforce strict VPN tunnels with multi-factor authentication, and disable legacy cleartext protocols (such as HTTP and Telnet) on controller management interfaces.
Objective 3 secret tips: Prioritize digital forensics artifacts such as system log files, authentication audit trails, network connection states, and firmware integrity hashes to reconstruct initial compromise vectors and timeline modifications.
You Should Know:
1. Securing Industrial Refrigeration Controllers and Web Interfaces
Step‑by‑step guide explaining what this does and how to use it:
To prevent unauthorized remote access to OT management interfaces, administrators must audit network perimeters and harden device configurations.
Step 1: Identify all exposed OT controllers on the network using port scanning tools like Nmap:
`nmap -p 80,443,8080 –open 192.168.10.0/24`
Step 2: Verify firmware versions against vendor security advisories (e.g., ensuring Danfoss AK-SM 800A controllers are updated to firmware R4.3.1 or later to mitigate authentication bypass and command injection vulnerabilities).
Step 3: Enforce HTTPS-only communication and restrict management access to dedicated internal VLANs or bastion hosts.
- Digital Forensics and Incident Response (DFIR) for OT Environments
Step‑by‑step guide explaining what this does and how to use it:
When investigating suspected tampering with temperature and defrost settings, forensic investigators must preserve volatile evidence from embedded controllers.Step 1: Capture live network traffic running across industrial protocols (such as Modbus TCP or BACnet) using Wireshark or tcpdump:
`tcpdump -i eth0 -w ot_traffic_capture.pcap`
Step 2: Extract system configuration files and audit logs from the controller management interface to check for unauthorized parameter changes or API command injections.
Step 3: Analyze timestamp anomalies in event logs to correlate sudden spikes in refrigeration temperature targets with external IP connection sessions.
- Network Segmentation and Firewall Hardening for OT/IoT Devices
Step‑by‑step guide explaining what this does and how to use it:
Proper zoning prevents lateral movement from compromised corporate IT networks into critical refrigeration and HVAC control loops.Step 1: Configure stateful firewall rules to block direct internet access to industrial controllers.
Step 2: Implement network segmentation rules via Linux iptables or enterprise firewalls to drop unauthorized inbound connections:
`iptables -A INPUT -p tcp –dport 80 -s 192.168.100.0/24 -j ACCEPT`
`iptables -A INPUT -p tcp –dport 80 -j DROP`
Step 3: Regularly audit rule bases to ensure zero unauthenticated exposure paths exist between public networks and operational controllers.
4. Firmware Verification and Vulnerability Assessment
Step‑by‑step guide explaining what this does and how to use it:
Proactive vulnerability scanning helps detect insecure web management interfaces before threat actors exploit them.
Step 1: Perform authenticated vulnerability scans using tools like Nessus or OpenVAS targeting OT asset ranges.
Step 2: Verify binary file integrity and check for hardcoded credentials or debug backdoors in older controller firmware images.
Step 3: Establish a strict patch management cadence for all embedded operational technology assets.
5. API Security and Command Injection Mitigation
Step‑by‑step guide explaining what this does and how to use it:
Web management interfaces often expose backend APIs susceptible to command injection if input sanitization is absent.
Step 1: Inspect HTTP POST/GET requests directed at controller web panels for suspicious shell metacharacters (e.g., ;, |, &).
Step 2: Implement robust input validation and parameter escaping within custom controller web applications.
Step 3: Deploy a Web Application Firewall (WAF) in front of critical facility management servers to intercept malicious payload injections.
6. Cloud and Remote Management Hardening
Step‑by‑step guide explaining what this does and how to use it:
Many commercial refrigeration units rely on cloud-connected management portals that require strict credential controls.
Step 1: Enforce hardware-token-based Multi-Factor Authentication (MFA) for all administrative accounts accessing remote monitoring dashboards.
Step 2: Review access control lists (ACLs) regularly to revoke stale vendor or contractor permissions.
Step 3: Monitor cloud API access logs for anomalous geographic logins or brute-force attempts.
- Continuous Monitoring and SIEM Integration for OT Systems
Step‑by‑step guide explaining what this does and how to use it:
Real-time alerting ensures rapid detection of abnormal physical setpoint changes caused by cyber intrusions.Step 1: Forward syslog and SNMP trap outputs from OT controllers to a centralized SIEM platform (such as Splunk or Elastic Stack).
Step 2: Create detection rules alerting on threshold breaches, such as unexpected continuous defrost cycles or rapid temperature escalations above safe storage limits.
Step 3: Conduct regular tabletop exercises simulating remote OT tampering incidents to test incident response readiness.
What Undercode Say:
Key Takeaway 1: OT security is no longer insulated by obscurity; exposing industrial refrigeration controllers directly to the internet bridges the digital-physical gap with catastrophic consequences.
Key Takeaway 2: Effective incident response in cyber-physical attacks requires correlating network artifacts, firmware vulnerability context, and physical operational logs.
The recent French supermarket refrigeration attack serves as a stark warning to critical infrastructure operators worldwide. By moving beyond logical IT safeguards and implementing rigorous OT network segmentation, strict firmware patch management, and continuous monitoring of environmental control parameters, organizations can mitigate the risk of remote physical sabotage. As industrial systems become increasingly interconnected, security teams must treat every remote management interface as a high-value target requiring defense-in-depth principles.
+1 Increased adoption of zero-trust network architecture across commercial refrigeration and HVAC sectors to prevent direct internet exposure.
+N Heightened risk of opportunistic threat actors weaponizing legacy IoT and OT firmware vulnerabilities for physical disruption.
+1 Mandatory regulatory standards enforcing strict access controls and vulnerability disclosure policies for industrial controller manufacturers.
 Related Video (86% Match):
 Let’s Practice For Free:
 Live Courses & Certifications:
Join Undercode Academy for Verified Certifications
 Request a Custom Project:
Secure, high-velocity infrastructure and disruptive technological engineering. Contact our engineering team for high-tier development and proprietary systems:
projects@undercode.co.uk
 Smart Architecture |
 Secure by Design |
 Trusted by Thousands
IT/Security Reporter URL:
Reported By: https://lnkd.in/p/d8rRgYaq – Hackers Feeds
Extra Hub: Undercode MoN
Basic Verification: Pass 
 JOIN OUR CYBER WORLD [ CVE News • HackMonitor • UndercodeNews ]
 Whatsapp
 Follow UndercodeTesting & Stay Tuned:
???? formerly Twitter  | @ Threads |
 Linkedin |
 BlueSky
The post Bridging IT and OT: Analyzing the French Supermarket Refrigeration Cyber Attack + Video appeared first on Undercode Testing.
Popular Products
-
 Electronic String Tension Calibrator ...
$41.56$20.78 -
 Pickleball Paddle Case Hard Shell Rac...
$27.56$13.78 -
 Beach Tennis Racket Head Tape Protect...
$59.56$29.78 -
 Glow-in-the-Dark Outdoor Pickleball B...
$49.56$24.78 -
 Tennis Racket Lead Tape - 20Pcs
$51.56$25.78